Why proxy-based SASE is giving mid-market IT teams a migraine
Let's face it: SASE (Secure Access Service Edge) was supposed to be the hot new thing. A unified framework that bundles networking and security into a…
2 June 2025
Let's face it: SASE (Secure Access Service Edge) was supposed to be the hot new thing. A unified framework that bundles networking and security into a sleek cloud-delivered model? Yes please! But somewhere along the way, for many, it's not living up to the promise.
Proxies: The return of a legacy villain
You'd think in 2025 we'd finally retired the old proxy playbook - yet here we are. Many SASE providers still rely on the same web proxy architecture that dates back to the dial-up modem era (OK, maybe not quite - but close), and your network traffic is trying to navigate through a maze of servers like a lost puppy in a park full of squirrels.
For mid-market organisations, this architecture is like using a fax machine to post a TikTok. It's outdated, clunky, and designed for a world that doesn't exist anymore.
Let's break down why.
Technical torture
Proxies introduce complexity by forcing all traffic through a central inspection point. That means:
-
Hairpinning traffic to a remote data centre - even if the destination is right next-door.
-
Latency spikes that make your team long for the simpler days of direct internet access.
-
TLS break-and-inspect policies that are more break than inspect, especially when certificate pinning or application incompatibility shows up.
I heard a customer describe their old proxy as "like trying to get from your desk to the office kitchen... but instead of walking 20 feet, you're required to take a flight to Paris, go through customs, and then return via Madrid before you're allowed a biscuit and a brew. Zero Trust, Zero Productivity more like!"
Your users don't care that traffic is "safely inspected by a cloud proxy node in Frankfurt." They care that Teams calls drop like flies (a recent podcast by Cisco highlighted the fact that packet loss as low as 1% can degrade service quality causing productivity headaches) or that SharePoint takes ten seconds to load a document.
Zero Trust, Zero Productivity more like!
Paying for the privilege of pain
Proxies don't just impact performance - they hit you where it hurts: your budget. They're like that friend who always suggests going the poshest restaurant in town, single-handedly consuming and entire bottle of Chateau Lafite Rothschild then asks to split the bill evenly! They're costly, they're high-maintenance, and they have a knack for making your CFO cry silently in the corner. We must not forget mid-market organisations don't have a "Cloud Transformation" budget comparable to the GDP of a small nation.
With legacy proxy-based SASE:
-
You're locked into expensive per-user pricing that doesn't scale for hybrid workforces.
-
You pay for infrastructure that's duplicative, like redundant DNS, threat protection, and SSL inspection tools you already have elsewhere.
-
You're investing in appliance-era thinking dressed up as cloud-native - an ironic twist on modernisation.
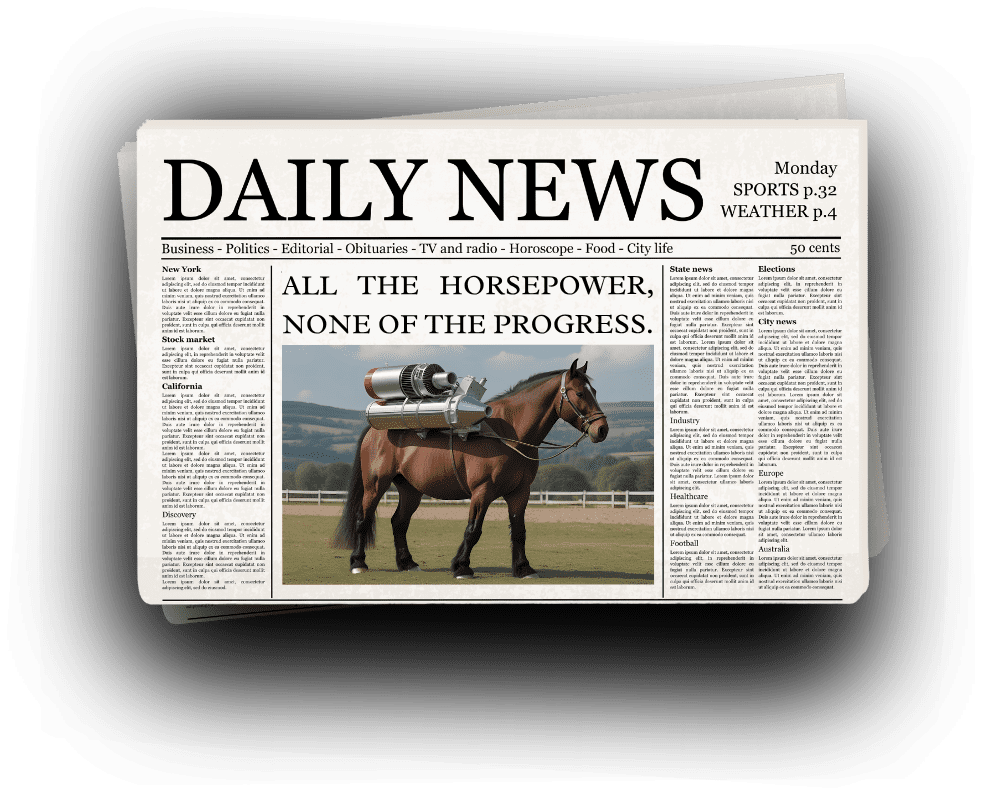
In short, it's like strapping a jet engine to a horse and calling it a futuristic mode of transport. The only saving grace is that between March and May 2025 at least seven major proxy providers introduced price reductions between 10-80% - even more of an indicator that they are trying to wring as much out of their architecture before it can no longer be resuscitated.
Operational overhead: the IT admin's lament
Running a proxy-based SASE model often feels like playing whack-a-mole with user complaints, policy conflicts, and mysterious 403 errors. Management is like juggling flaming chainsaws while riding a unicycle - it's a spectacle, but it's not sustainable.
Every update means:
-
Relearning arcane rule sets.
-
Cross-team calls to figure out why traffic is blocked to mycriticalbusinessapp.com
-
Endless maintenance windows, patches, and false positives.
In the meantime, your overworked IT team is dreaming of simpler times - like when all they had to do was manage Active Directory.
Enter TrustLayer: proxy-free, hassle-free
We've decided enough is enough. We believe mid-market cybersecurity shouldn't be:
-
Built on 1990s tech
-
Priced like enterprise software
-
So complex that even your CISO avoids asking how it works
Our approach is simple:
-
A proxyless architecture that inspects traffic inline and enforces policies locally without detours
-
Cloud-delivered controls that scale with your workforce, not against it
-
Lower TCO without sacrificing enterprise-grade security
It's time to stop retrofitting legacy proxies into a modern security world. Let's build solutions that fit the mid-market, not fight it. Because honestly, nobody wants a pain in the SASE, and let's face it, life's too short to deal with the uncool uncles of cybersecurity.
TrustLayer has been instrumental for us in creating a robust security posture... The setup was a piece of cake - seriously, it was a breeze - and most of our needs were addressed right from the get-go... The centralised management and intuitive interface save me a ton of time and headaches.
Mark Jones IT Director, Veramed
Policy by user, group or tool, applied by action: uploads, shares, downloads.
Already running Barracuda or Forcepoint? We publish an honest side-by-side, including where they win.