What is AI Exposure?
AI Exposure is the part of TrustLayer Browse that governs AI tool use. It finds the generative AI tools your staff use in the browser on company devices, sanctioned or not, marks each one approved or unapproved, risk-scores the actions inside it, and applies a policy of allow, block or track by action, user or group.
It is not a separate module. The existing Web Security and CASB modules already identify when people use AI tools, through what's already on your devices. No proxy, nothing new in the traffic path. It draws on a catalogue of 2,000+ cloud apps and 8,000+ risk-rated actions, with the AI tools flagged.
Supported AI activity is logged by user, device, application, action, risk level and outcome. When the insurer, the auditor or the board asks how you govern AI, you export the report.
Three steps. No project.
Web Security and CASB together give you AI Exposure. Both already? Skip to step 2. Web Security only? Add CASB through BT, your MSP or reseller. Same install, same invoice.
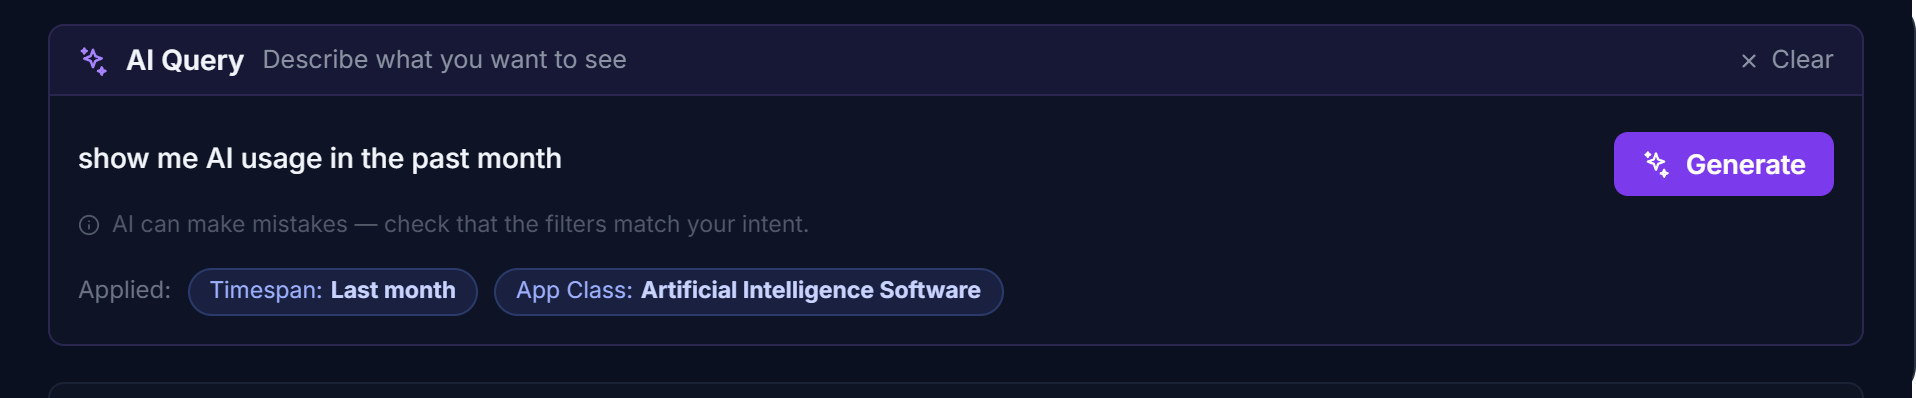
Request your AI Exposure report. It comes from logs you already have: AI tools used across managed browsers, by whom, with a risk score per action.
Mark the tools you sanction. Allow those. Block the ones you don't. Track everything else. Per action: open, sign in, send a message, upload, share. We'll help write the first set.
Three outcomes. Per action, user or group.
Block, allow, or allow and track. The same policy engine you use for web and cloud apps: conditions combine with AND/OR logic across user, group, device, network, location, time and risk level.
Block and warning pages are customisable per policy. A warn rule can explain the risk, point people at your approved tool and let them continue, with the activity logged.
It sees what you tell it to see.
Every action is a switch. Track it, block it, or turn tracking off. If prompt privacy matters in your organisation, set the chat action to not track and you still see the tool, the user and the uploads.
Nothing changes.
Except you can see it.
Same console, same agent, same account team. What you gain is the inventory, the risk score and an answer to the question the insurer started asking this year.
Asked by customers before they ask for the report.
Do I need to install or enable anything?
No. If you run Web Security and CASB, the data is already being collected. Ask us for the report, or sign in and query the logs yourself. If you only have Web Security, add CASB; it uses the agent already on your devices.
Does it read what people type into AI tools?
In the browser, it can. Prompts sent to a web AI chat are logged as an action. If you would rather not record them, set that action to not track: you still see the tool, the user, the account and any uploads. Native desktop and mobile apps are not inspected.
Can it block ChatGPT but allow Copilot?
Yes. Mark Copilot sanctioned and allow it; leave ChatGPT unsanctioned and block or track it. Rules apply per tool, per action and per user or group, so a marketing team can be allowed what finance is not.
Will it slow the laptops down?
No. Policy is enforced by what's already on the device. There is no proxy and nothing new in the traffic path.
Does it coach people or suggest a safer tool?
Yes, if you set it up that way. Block and warning pages are customisable per policy, a warn rule can show your own message, explain the risk, point people at the approved tool and let them continue with the activity logged. A hard block stays a block.
Will it help with Cyber Essentials or the insurance renewal?
Yes. Cyber Essentials' 2026 question set brings AI tools into scope like any cloud service: declared, known to IT. Insurers increasingly ask about AI use directly. AI Exposure gives you a dated record of the tools in use and the policy applied to each, exportable in one report.
Add CASB to what you have, or start with the whole Browse layer. From the device. Live in 30 minutes.